Enterprise brands trust Magnolia DXP


Access our complete compliance portfolio, including ISO 27001, SOC 2, SOC 3 and ENS certifications, directly through our self-service portal. The Trust Center provides real-time visibility into our security posture, sub-processors, and vulnerability management policies and coordinated vulnerability disclosure process. Security issues can be reported through our Trust Center; our process is aligned with ISO/IEC 29147 and the CRA vulnerability-reporting requirements applicable from 11 September.
Secure every layer without slowing your teams down
From how users sign in to how AI agents operate and where your infrastructure runs, Magnolia DXP builds governance into every layer of the stack — combining enterprise control with the speed your teams need to move.
GENERAL SECURITY
Confirm who signs in. Control where they can go
Generic authentication doesn't fit an enterprise identity stack. Magnolia DXP's foundational security controls are built to work with the directory, network, and site setup you already have.
- Flexible authentication: Connect to your existing directory setup, including LDAP, certificate-based logins, or CAS single sign-on, instead of managing authentication from scratch.
- Cross-site security: Run multiple sites from one Magnolia DXP instance while keeping content reachable through the right domain, avoiding SEO penalties for duplicate content.
- Configurable access controls: Restrict access down to specific IP ranges or request types when your security policy calls for it.
IDENTITY & ACCESS
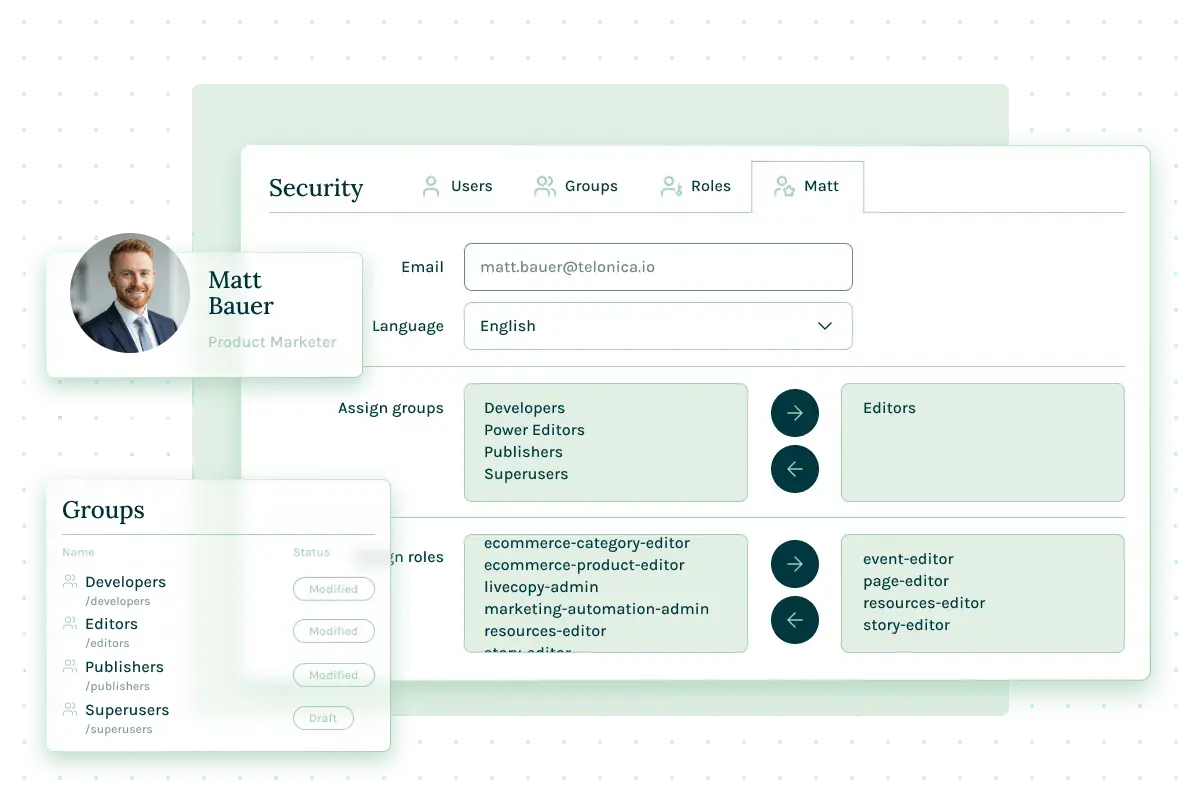
Centralized identity and access management
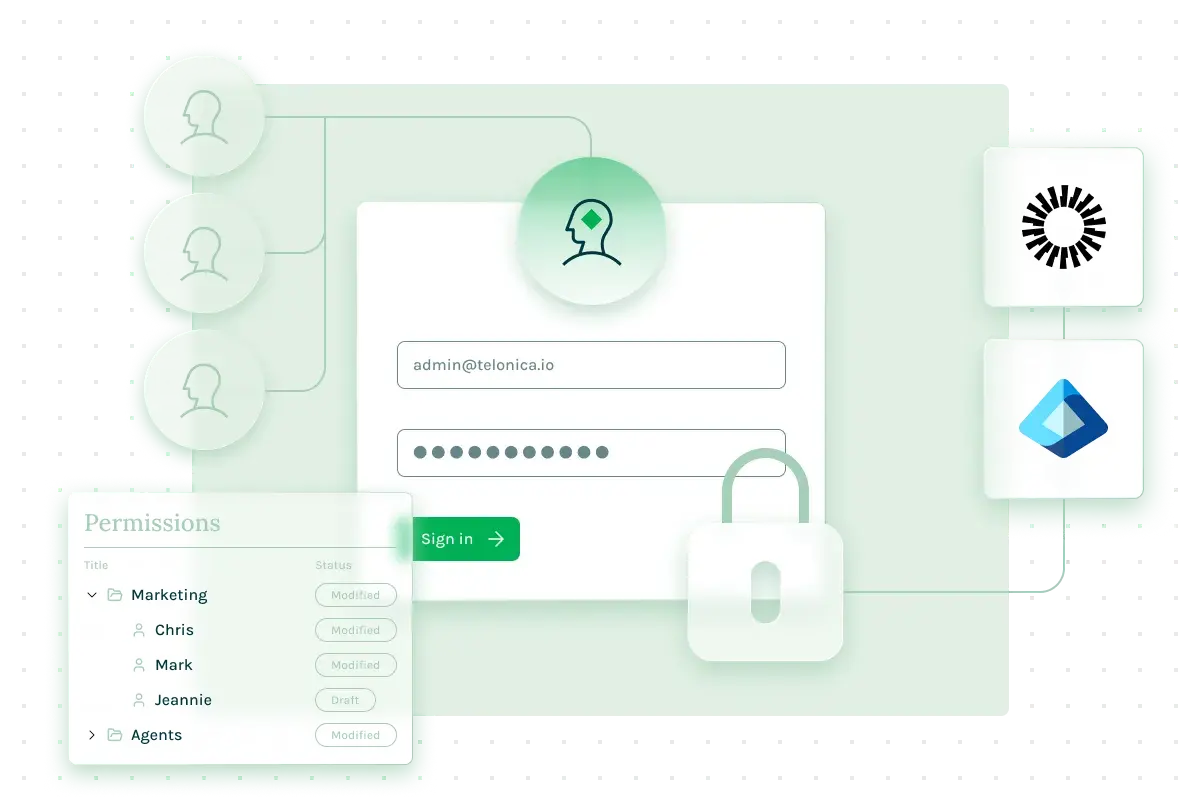
Magnolia DXP supports enterprise security policies through comprehensive SSO and IdP federation, so access decisions stay tied to the directory you already manage.
- Federated identity: Created on first login, with roles and groups re-mapped from your IdP every login, so removing someone from your directory ends their access at the next request.
- Broad IdP support: Integrates with major identity providers (e.g., Okta, Microsoft Entra ID) via SAML 2.0 and OIDC, removing the need for custom authentication development.
- Granular governance: Define scope-based permissions for editors and administrators, so content stays secure without slowing editorial workflows.
AI SECURITY
Scale AI. Keep humans in control.
AI agents only earn trust if they operate inside real limits. Magnolia DXP's agents are governed by design, not by policy documents nobody reads. Magnolia DXP doesn't build or train its own AI models. Agents connect to your choice of third-party providers, such as OpenAI, Anthropic, and AWS Bedrock, through Magnolia AI Connector framework, so this governance applies no matter which model is doing the work.
- Human-in-the-loop validation: Agents can stage drafts, but publishing is disabled by default. Automated actions still route through your team's existing approval workflow.
- Three-layer security framework: Each agent skill runs within its own restrictions, bounded by role-based access control, and subject to module-level deactivation.
- Audit logging: Tool executions, queries, and system changes are logged, giving compliance teams the traceability they need.
CLOUD SECURITY
Automate protection. Shrink your blind spots.
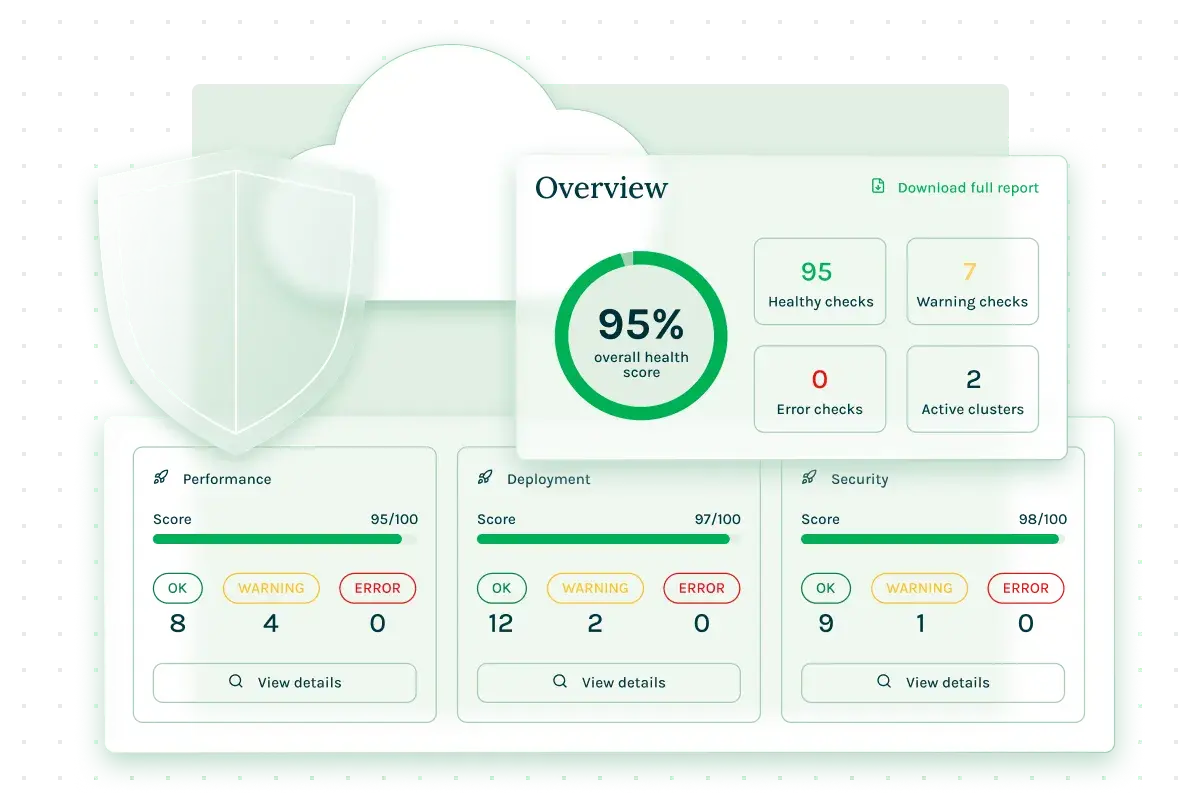
Security stops working the moment it depends on someone remembering to turn it on. Magnolia DXP builds enterprise-grade defense into the platform, with advanced controls available as an add-on.
- Automated edge-level defense: Traffic is filtered at the edge via Fastly's CDN, blocking Layer 3, 4, and 7 DDoS attacks with a managed, OWASP-based rule set before they reach your origin servers.
- Deployment integrity: Custom code is scanned before deployment, and every storage volume is encrypted at rest by default.
- Defacement defense (Advanced Security): Public pages are monitored 24/7 to detect and flag unauthorized changes.
Compare
Magnolia’s security tier comparison
- Included
- Excluded
| Security aspect | Standard Security | Advanced Security |
|---|---|---|
| CDN Security | ||
| DDoS Mitigation and Protection | Layer 3, 4 & 7 | Layer 3, 4 & 7 + advanced edge rate limiting |
| WAF | Default Rule Set | Custom Rule Set |
| Bot Protection Service | Excluded | Included |
| AI Traffic Management | Excluded | Included |
| Data Security | ||
| Encryption Key Storage | Key owned by cloud vendor or Magnolia | Key owned by customer |
| Active Threat Monitoring | Excluded | Included |
| Vulnerability Scanning | Docker image scanning | Isolated pipeline environment |
| Operational Security | ||
| Malware Detection | Excluded | Included with ClamAV installation |
| Web Defacement Protection | Excluded | Included |
| Secure Cluster Communication Traffic | Excluded | Included |
| Security Testing | ||
| External Penetration Test | Optional | Included |
Magnolia DX Cloud Security
Our customers rely on Magnolia’s cloud web content management software to serve thousands of digital experiences every day. This page provides an overview of our certifications and processes to ensure the security of their data and the availability of their services.

Advanced Security Product Brief
Take the security of your custom Magnolia cloud solution and your data to the next level.
CASE STUDIES
Stories of security and success


Connected Capabilities
A complete platform for global growth
See how your team can evolve its capabilities.


Talk to our experts
Get a security review for your stack
Talk to our security experts about how Magnolia DXP fits your compliance requirements, your identity stack, and your architecture — not a generic questionnaire.
- Walk through your specific compliance requirements
- See the identity and access model in your environment
- Get a clear answer on what tier and setup you need
FAQs